Enterprise data is becoming more valuable, more distributed and often harder to govern.
Organisations now generate and retain huge volumes of customer information, intellectual property, operational records, analytics data and AI datasets. At the same time, regulatory requirements are evolving, workloads are spreading across multiple environments, and businesses need to know exactly where important information is stored, who can access it and which jurisdictions apply.
This is why data sovereignty storage is becoming an important part of enterprise infrastructure planning.
Storage is no longer simply somewhere to keep information. Businesses increasingly need to consider where data physically resides, how it moves between environments, who administers the underlying infrastructure and how much direct control the organisation retains.
For some workloads, public cloud will remain the right choice. Others may benefit from on-prem data storage, private infrastructure or hybrid architectures that give organisations tighter control over sensitive information.
What is data sovereignty?
Data sovereignty is the principle that data is subject to the laws, governance requirements and regulatory frameworks associated with the jurisdictions in which it is stored, processed or controlled.
For businesses, this involves more than knowing which data centre contains a particular dataset.
A data sovereignty strategy should consider where information is physically stored and processed, who administers it, which organisations can access it, which jurisdictions apply and how data moves between locations.
It also needs to consider security, backup, retention and deletion.
This is where data sovereignty and data security overlap. Security focuses primarily on protecting information against unauthorised access, loss, alteration or destruction. Sovereignty asks broader questions about location, control and jurisdiction.
Highly encrypted data could still create a sovereignty issue if it is stored or processed somewhere that does not meet the organisation's legal, regulatory or contractual requirements.
Equally, information can remain within an approved country but still be poorly secured.
Strong data sovereignty solutions therefore combine governance and infrastructure with appropriate security controls.
What is the difference between data sovereignty and data residency?
Data sovereignty and data residency are closely connected, but they are not interchangeable.
Data residency describes where information is physically stored or maintained. Data sovereignty considers the wider legal, jurisdictional and governance framework affecting that information.
For example, an organisation may require customer records to remain within the UK or European Union. That is principally a residency requirement.
Sovereignty goes further. It asks who can administer the infrastructure, which legal jurisdictions apply, whether information can move elsewhere and what happens to backups, replicas and archived copies.
|
Area |
Data residency |
Sovranità dei dati |
|
Primary concern |
Where data is located |
Who controls data and which laws or governance requirements apply |
|
Infrastructure focus |
Physical storage location |
Location, administration, access, processing and jurisdiction |
|
Typical question |
"Which country is our data stored in?" |
"Where is our data, who controls it and under whose jurisdiction?" |
|
Ambito |
Relatively narrow |
Wider infrastructure and governance issue |
|
Relationship |
Can form part of a sovereignty strategy |
Can include residency alongside legal, technical and operational controls |
Residency can therefore form an important part of sovereign data infrastructure, but keeping information inside a particular territory does not automatically satisfy every sovereignty requirement.
Why does data sovereignty matter for enterprise storage?
Storage is one of the most persistent parts of enterprise IT.
Applications change. Virtual machines come and go. Compute resources can be provisioned and removed quickly.
Data often remains for years.
Customer records, databases, backups, archives, AI training datasets, security telemetry and intellectual property may also exist in several locations at once.
That makes storage fundamental to enterprise data control.
Organisations need to be able to answer questions such as:
- Where does sensitive information reside?
- How many copies exist?
- Which users and systems can access it?
- Does it leave an approved jurisdiction?
- Where are backups and disaster recovery copies maintained?
- How long is information retained?
- Can it be deleted when policy requires?
- Can the organisation demonstrate these controls to auditors or regulators?
Storage architecture therefore has a direct bearing on how easily an enterprise can govern its information.
How can on-prem storage support data sovereignty?
On-prem data storage can support data sovereignty by giving organisations greater direct control over where systems are located, how they are administered and who can access them.
When storage operates within an organisation's own data centre or another specifically controlled facility, its physical location can be defined precisely.
Businesses can also establish their own policies around identity, encryption, network segmentation, retention, remote administration and infrastructure access.
Keeping processing closer to storage can reduce unnecessary movement of sensitive information too. This is increasingly relevant for AI, analytics and other data-intensive workloads where moving large proprietary datasets between local systems and remote environments can create additional cost, latency and governance considerations.
However, on-premises infrastructure is not automatically sovereign.
A storage system can sit inside a company's own building while still being badly governed. Organisations also need to consider privileged access, encryption keys, backup destinations, replication, remote management, maintenance, disaster recovery, monitoring and secure deletion.
The objective is therefore controlled infrastructure, not simply locally installed infrastructure.
On-premises, cloud or hybrid: which provides greater data control?
There is no single architecture that satisfies every data sovereignty requirement.
The right model depends on the sensitivity of the information, regulatory requirements, internal expertise, workload characteristics and the degree of direct control required.
|
Consideration |
On-premises storage |
Public cloud storage |
Hybrid infrastructure |
|
Physical data location |
Can be tightly defined |
Depends on provider region, service and configuration |
Can be defined separately by workload |
|
Direct infrastructure control |
Alto |
Underlying infrastructure is provider operated |
High for selected workloads |
|
Data residency |
Relatively straightforward with fixed locations |
Requires careful regional configuration |
Sensitive datasets can remain in controlled locations |
|
Scalabilità |
Requires capacity planning |
Highly elastic |
Combines local capacity with cloud scalability |
|
Operational responsibility |
Primarily the organisation |
Shared with provider |
Shared across environments |
|
Movimento dei dati |
Can remain predominantly local |
May move between users, services or regions |
Policies can determine what may move |
|
Governance |
Centrally controlled |
Requires understanding provider controls and contracts |
Requires consistent policies across environments |
|
Typical fit |
Sensitive data and direct-control workloads |
Elastic or distributed applications |
Estates containing workloads with different sovereignty requirements |
This should not be interpreted as "controlled on-premises" versus "uncontrolled cloud". Major cloud platforms provide extensive governance and security capabilities, while poorly administered on-premises infrastructure can create significant risk.
The key question is whether the chosen architecture enables the business to meet its particular location, access, jurisdiction, security and availability requirements.
How can businesses keep sensitive data under direct control?
Greater enterprise data control starts by understanding the data itself.
Not every dataset needs identical treatment. Public marketing files and temporary development data have very different requirements from customer records, financial information, regulated data or commercially sensitive intellectual property.
A practical data sovereignty storage strategy should therefore include several steps.
1. Classify important data
Identify which information is public, internal, confidential, regulated or highly restricted.
Classification allows stricter controls to be applied where they are actually needed rather than treating every byte identically.
2. Map where every copy resides
Do not stop at primary storage.
Map backups, snapshots, replicas, archives, disaster recovery systems, development environments, cloud storage and edge locations as well.
A primary database may comply with residency policy while an overlooked backup does not.
3. Define approved locations
Create clear rules governing where each class of information may be stored and processed.
These policies may specify facilities, countries, economic regions, cloud regions or approved service providers.
4. Control access
Sensitive information should only be available to authorised users, applications and administrators.
Role-based access, least-privilege policies, strong authentication and effective monitoring all contribute to secure enterprise storage.
5. Protect the complete data lifecycle
Consider data while stored, moving across networks, being backed up and eventually deleted.
Infrastructure security, encryption, resilient backups and secure erase capabilities should form part of the overall architecture.
6. Review data placement regularly
Data estates change constantly.
New services appear, applications migrate and datasets grow. Businesses should periodically verify that real-world data placement still matches policy.
What role does storage infrastructure play in regulatory compliance?
Storage infrastructure does not make an organisation compliant by itself.
Compliance depends on governance, policies, security, people, processes and the specific regulations applying to the organisation.
Storage does, however, provide part of the technical foundation needed to enforce those policies.
A well-designed storage environment can help control where information resides, where replicas are created, how long information is retained, who can access it and how data is protected or deleted.
This makes storage infrastructure an important consideration during compliance planning, rather than something that should be designed afterwards.
Infrastructure teams should therefore work alongside security, risk, legal and compliance functions when determining where sensitive information will reside and how it will be managed.
Can hybrid infrastructure help meet data sovereignty requirements?
Yes. For many businesses, the most practical architecture will be neither exclusively cloud nor exclusively on-premises.
Hybrid infrastructure can support data sovereignty by allowing workloads and datasets to be placed in different environments according to their individual requirements.
Sensitive or regulated information might remain within controlled on-premises infrastructure, while less restricted applications use public cloud services.
An organisation could also retain an authoritative dataset locally while using appropriately governed cloud resources for workloads that require additional elasticity.
The important point is that workload placement should be deliberate.
Businesses should determine whether a dataset has residency restrictions, whether it can legally or contractually cross jurisdictions, where backups will reside, who can administer each environment and how policies will remain consistent.
A hybrid strategy should not simply mean that information has accumulated across several platforms without a clear governance model.
Building sovereign data infrastructure with Western Digital enterprise storage
Greater control is useful only if infrastructure can still meet enterprise capacity, performance and availability requirements.
Modern organisations may need to store petabytes of information for databases, AI, analytics, backups and archives. Sovereign data infrastructure therefore needs to be scalable as well as controlled.
Western Digital's current data-centre portfolio includes Ultrastar enterprise HDDs and high-density storage platforms designed for large datasets and demanding workloads. Its Ultrastar Data Series JBOD platforms support software-defined and disaggregated storage architectures, allowing storage capacity to be scaled separately from compute. Current configurations can provide up to 3.26PB of scalable storage.
This demonstrates an important point: choosing on-premises or sovereign infrastructure does not have to mean accepting small-scale infrastructure.
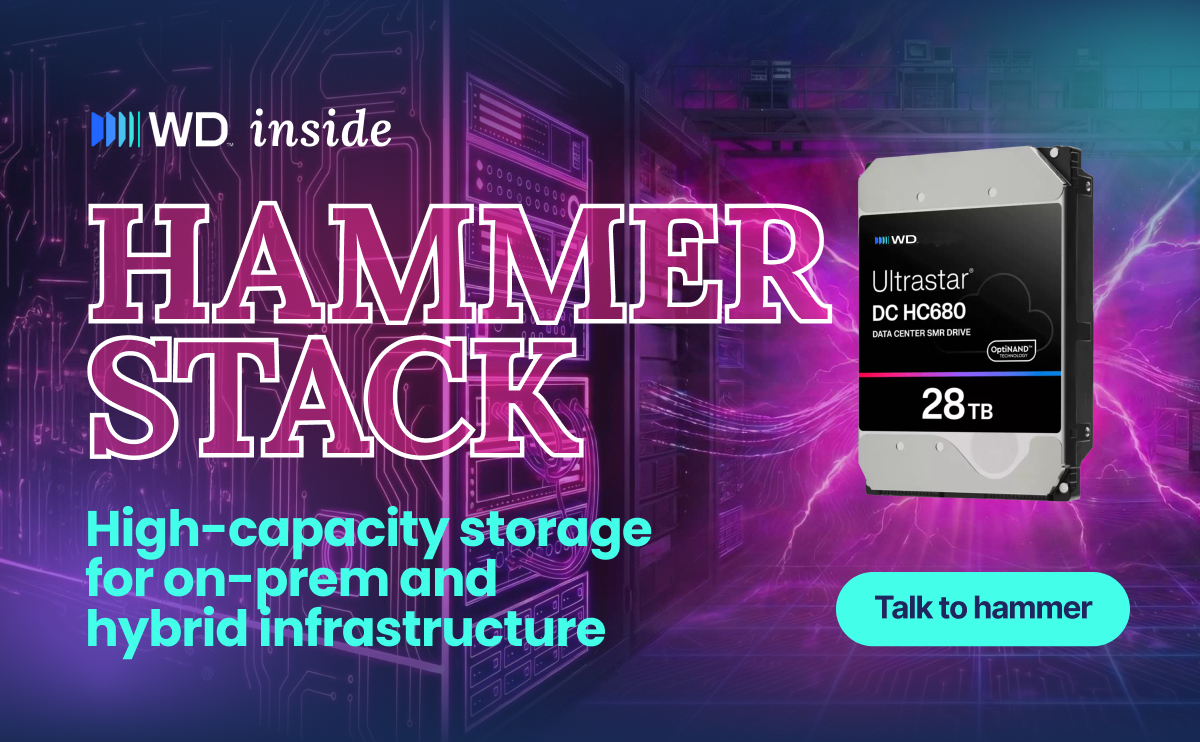
Western Digital also forms the storage layer within Hammer Stack, where it is positioned to keep datasets and model artefacts local while supporting predictable performance and reducing exposure to variable cloud storage and egress costs.
Hammer Stack combines this storage foundation with compute, networking and data-platform technologies to support workloads that organisations choose to operate on-premises for control, performance or sovereignty reasons. Subscription and leasing options are also available, providing an alternative to both large upfront infrastructure investment and entirely cloud-based consumption.
The wider Hammer enterprise storage portfolio spans flash, hybrid, object, software-defined and data-centre storage, alongside backup, recovery and resilience technologies.
The result is greater choice around where enterprise data resides and how infrastructure is designed around it.
Greater enterprise data control starts with knowing what you control
Data sovereignty does not mean every workload needs to return to an on-premises data centre.
Nor is public cloud inherently incompatible with sovereignty requirements.
The real objective is intentional control.
Businesses need to know what information they hold, where every important copy resides, who can access it, how it moves and which infrastructure model provides the appropriate level of governance.
For particularly sensitive datasets, that may mean on-prem data storage or dedicated sovereign infrastructure. Other workloads may be well suited to public cloud. For many organisations, hybrid infrastructure will allow both approaches to coexist.
With scalable Western Digital enterprise storage supporting the underlying data layer and approaches such as Hammer Stack providing another route to controlled on-premises infrastructure, businesses can design storage around sovereignty, performance, capacity and operational requirements rather than treating data location as an afterthought.
Ultimately, greater enterprise data control begins with a simple requirement: know where your data is, know who controls it and ensure your infrastructure keeps those answers clear as the organisation grows.